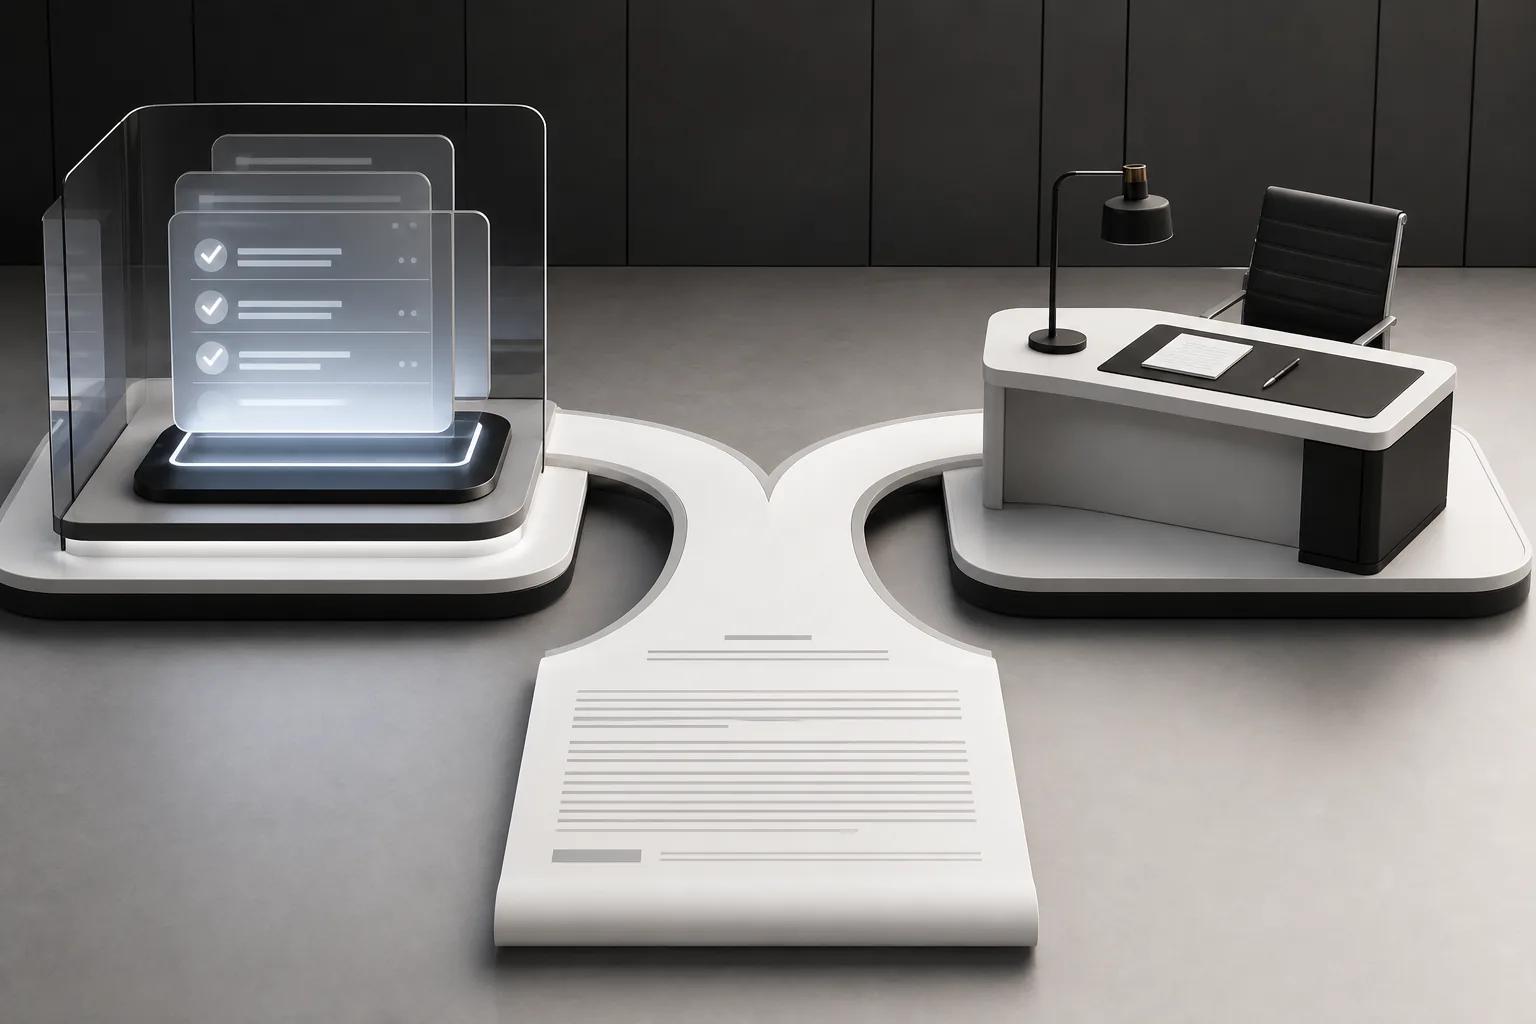
AI can cut the time your legal team spends on routine review, but a fast answer is no use if you can't show where it came from. AI automation for legal compliance works best when you start with one defined task, clear data limits, and a human who owns the final call.
Use these five steps to move from a manual process to a controlled workflow your team can test, explain, and maintain.
Step 1: Map the Compliance Obligations and Owners
Start by listing the rules and internal commitments the workflow must support. Then name the people who own each obligation and the evidence that proves it was met.
Choose one work area, such as contract review, legal intake, or regulatory change tracking. For each obligation, record the source, the affected process, the control in place, and the role accountable for it. Add the system where the proof lives, such as a matter file or approved policy store.
Keep the map specific. “Review vendor terms” is too broad to test. “Flag a missing data-use restriction in a vendor agreement and send it to counsel” gives the team a clear task and a review point.
Separate legal requirements from internal preferences. A preferred clause may be a useful review rule, but it isn't automatically a legal duty. This distinction helps prevent an AI workflow from presenting a business choice as a legal conclusion.
A tiered approach to AI use is a useful design principle for legal teams: match review and controls to the workflow’s impact, rather than treating every use as equally risky.
For a working template, use an AI compliance requirements map to connect system inputs, decisions, approval roles, and records. Zylo Technologies can help your team turn that map into a build plan when the workflow crosses several systems or owners.
By now, you should have a short obligation register with a named owner and a proof source for each item. If an obligation has no clear owner, pause before automating it.
Step 2: Choose a Bounded Workflow and Define Its Risk
Pick a task with repeatable inputs and a reviewable result. AI automation for legal compliance is a poor fit for work where the system must make a final legal judgment or act on facts it cannot verify.
Good starting points include extracting dates and clauses from standard agreements, sorting incoming documents, or drafting a first-pass summary for counsel. Repetitive routing can often use ordinary automation rules. Add AI only where language varies enough that fixed rules struggle, such as finding a renewal term written in different ways.
Score the task by asking four questions: How sensitive is the data? How much harm could a wrong result cause? Can the decision be reversed? How easily can a person check the output against its source?
Use the answers to set limits. A system that identifies a missing clause can open a review task. It shouldn’t approve the contract or send a legal position to a counterparty without an authorized person’s sign-off.
Vendor claims need the same scrutiny. Some tools focus on contract analytics, while others describe regulatory monitoring or requirement mapping. Check any stated source trail and its relevance before relying on it.
Write a short risk statement before choosing software: what the workflow may do, what it must never do, and what happens when it’s uncertain. A compliance checklist for AI automation can help keep those boundaries visible during tool selection.
By now, you should have one pilot workflow, a written risk level, and a clear stop point. Keep the first release narrow enough that a reviewer can inspect every result.
Step 3: Design the Automation, Data Boundaries, and Controls
Build controls into the workflow before connecting a model. Decide which data it can read, which actions it can take, and what record it must leave behind.
Start with data access. Give the workflow only the files and fields it needs. In legal work, access should follow matter permissions, not just a broad team folder. Keep client-confidential material out of unapproved tools, and confirm how the vendor handles prompts and outputs before sending sensitive content.
Next, keep the automation path plain and testable. A typical contract review flow might receive a file, check its matter access, extract defined clauses, compare them with an approved playbook, and route exceptions to counsel. Keep each stage distinct so a failure in extraction doesn’t look like a clean review.
Ask the model to return the source passage with each finding. If it flags a clause, the reviewer should be able to open the exact text that triggered the flag. If the source is missing or the clause is unclear, the workflow should mark the result as unresolved instead of filling the gap with a guess.
Set permissions by action. Read-only access is enough for many review tasks. If a workflow can update a matter record or send a message, put that action behind a separate approval gate. Keep test and production access apart, and make it possible to pause the workflow quickly.
For regulatory monitoring, use approved data channels where available and preserve the source ID and retrieval time. A compliance monitoring agent design can help frame how evidence moves from a source to a finding and then to an owner.
Zylo Technologies approaches this as a systems problem, not a prompt-writing exercise. The durable part is the permission model, connectors, exception path, and audit record around the model. An impressive prompt is not a product.
By now, you should have a workflow diagram that shows data access, model use, approval gates, and failure states. Review it with legal, security, and the system owner before building.
Step 4: Pilot the Workflow With Human Review and Failure Tests
Run the pilot beside the current process before letting it handle work on its own. Have a qualified reviewer check the AI output against the source document and record whether they accepted, edited, or rejected it.
Build a test set from approved examples. Include ordinary files, a missing page, conflicting terms, an unreadable scan, and a document that falls outside the workflow’s scope. For each case, write down the expected result before running the system. That makes it easier to spot a confident but wrong answer.
Test the whole path, not only the model’s summary. Confirm that the right file reaches the workflow, the right matter permissions apply, the output points to the source, and any exception reaches the right owner. Also test what happens when a connected system is down or the model returns nothing useful.
Keep human review meaningful. Give reviewers the original text, the extracted finding, and enough context to accept or correct it. A button that says “approve” is not a safeguard if the person can’t see the evidence behind the result.
Track review time and quality together. A shorter first pass is useful only if counsel still catches key omissions. Watch for repeated edits, missed clauses, false alarms, and cases where staff work around the designed process.
For an AI pilot, keep evidence of the test cases, reviewer actions, and fixes so the team can show how the control operated.
When the system fails, make the safe path obvious: stop the run, route the item to a person, and preserve the record. Don’t let a missing source or low-confidence result quietly pass as a successful review.
By now, you should have pilot results, a list of known failure modes, and a decision on whether to revise, expand, or stop. Set the pass criteria before you look at the outcome.
Step 5: Deploy With Monitoring, Evidence, and Change Control
Move the workflow into production only when its owner, controls, and monitoring plan are clear. Deployment is the start of ongoing oversight, not the end of implementation.
Log each run with enough detail to reconstruct it later: the matter or record involved, source documents, model and workflow versions, output, reviewer, and final action. Protect the log as sensitive information, and set a retention period that fits your organization’s policy and legal needs.
Monitor the work, not just uptime. Review whether the system is missing relevant clauses, sending too many routine items to counsel, or failing to route exceptions. Sample outputs against the source on a schedule that fits the task’s risk. A change in document types or policy language may require new tests.
Define what triggers a review. A model update, new data source, permission change, or expanded use case can alter the risk. Record who approves each change, what tests they ran, and whether the team needs to update training or user instructions.
Keep an incident path. If the system exposes restricted data or sends an incorrect legal communication, staff should know how to stop new runs and notify the right owner. Preserve the relevant workflow logs so the team can investigate what happened.
Use a simple operating record: current owner, approved purpose, permitted data, connected systems, test date, open issues, and next review date. Zylo Technologies’ governance and risk services can support teams that need to align workflow controls with a wider control program.
By now, you should have a named production owner, a live monitoring routine, and a change log. If no one has time to review exceptions, the workflow isn’t ready to scale.
FAQ
What legal tasks can AI automate safely?+
AI can help with repeatable tasks such as sorting documents, extracting dates, comparing standard clauses, and drafting summaries for review. In AI automation for legal compliance, keep the system’s role limited to preparation or routing when the outcome needs legal judgment. A qualified person should verify findings before they affect a client, contract, filing, or formal compliance decision.
How do you prevent AI from making up legal answers?+
Require the workflow to cite the source passage for each material finding, then test it with cases where the answer is missing or unclear. Keep approved source material current and route unsupported claims to a person. AI automation for legal compliance should show “unable to verify” rather than infer a legal conclusion from incomplete context.
Does a lawyer need to review AI contract analysis?+
Yes, when the analysis could affect legal rights, contract terms, or a client’s position. AI can flag language and point to a passage, but a lawyer or authorized contract reviewer must assess context and decide what to do. Set the review level based on the clause’s impact and the workflow’s tested performance.
How should a legal team measure an AI compliance pilot?+
Measure both time and quality. Compare review time with the current process, then track missed issues, incorrect flags, reviewer changes, and failed handoffs. AI automation for legal compliance should also leave enough evidence to explain each result. Don’t expand the pilot just because it runs faster if reviewers find the same important errors.
Conclusion
Start with one bounded workflow, give it the least access it needs, and keep a person accountable for decisions that carry legal risk. Write down the workflow’s limits and pass criteria this week; if your process spans several systems, Zylo Technologies can help scope the architecture and controls before a build begins.
Share this article
About the author
Professional Intro Operational Architect focused on operationalizing AI across business systems
Author at Zylo
Phil Slorick is an Operational Architect focused on helping organizations integrate AI into business systems and workflows. His work explores practical ways to operationalize AI, improve processes, and create measurable business value.