AI projects get hard to govern when teams can’t say what’s running, who owns it, or when a person must step in. An AI automation governance framework turns those questions into working rules. Published frameworks list the parts of AI governance, but your team still needs to assign owners and put each rule into daily work.
We analyzed 33 comments and questions from YouTube and Quora about AI automation governance frameworks and found that 27% mentioned how to meet AI regulatory standards.
Step 1: Set the scope of your AI automation governance framework
Start with an inventory of every AI system and automated workflow your organization uses. Include pilots, third-party services, internal tools, and systems built by individual teams. A small pilot can still touch sensitive data or affect a customer, so don’t limit the list to systems already in production.
For each entry, record its purpose, business owner, technical owner, data sources, connected systems, and current stage. Add the model or service version when known. Note whether the workflow makes a recommendation, drafts content, or takes an action. Those distinctions help you decide what oversight it needs.
A useful inventory describes a system well enough for someone outside its build team to understand what it does. If a workflow reads support messages and drafts replies, record which messages it can access and whether an employee checks each reply. If an agent can change a record, name the system and the types of changes it may make.
Your inventory should also capture where the system runs and how it gets information. That gives security and operations teams a way to trace data movement and spot unapproved connections. A living inventory is more useful than a spreadsheet updated once a year. Connect it to the intake and release process so changes prompt a review.
An AI inventory assessment can identify systems using AI or machine learning and reveal ethical risks. Governance bodies create, implement, and enforce guidelines for AI development and use. Transparency supports trust in AI systems, while accountability establishes clear responsibility for AI decisions. Algorithmic bias prevention and privacy protection are also governance concerns.
Use the inventory to set a boundary for your program: which workflows are covered, which teams must follow the rules, and who can approve an exception. Our AI governance framework guide covers the broader program design; this inventory is the working record your team will update as systems change.
At Zylo Technologies, we treat that inventory as part of the system design, not a document to finish after launch. Our senior-only delivery pods build AI agents and automation systems with the operating context in view.
Milestone: You should have a current list of systems, named owners, and enough detail to assess each workflow’s impact.
Step 2: Classify workflows by risk and set approval thresholds
Classify each workflow by the harm a wrong action could cause, not by how advanced its model seems. A system that drafts an internal meeting summary has a different impact from one that changes customer access or recommends a decision about a person.
Use a short set of questions at intake. What data does the workflow read? Who could be affected by an error? Can it take an action without review? Can the action be reversed? A high-impact answer should raise the workflow’s review level. Record the reason for the rating so another team can understand the decision later.
The table below is a starting policy, not a universal legal risk scale. Set your own categories with the teams responsible for the systems and the people affected by them.
Set approval thresholds in terms of actions, not vague confidence language. For example, specify which account changes need a second person’s approval, or which uncertain cases must go to a trained reviewer. Avoid setting a numerical confidence cutoff unless your team has tested what that number means for the task.
Privacy protection and algorithmic bias prevention are governance components. Teams can consider data minimization, informed consent, testing, and monitoring in review questions, such as whether a workflow uses only the data it needs. Privacy and bias practices can help turn broad goals into review questions.
For US teams, map the rules to applicable federal and state obligations, including privacy requirements that apply to your data and use case. NIST AI RMF can help organize risk work around Govern, Map, Measure, and Manage. ISO 42001 offers a management-system standard for AI. Neither replaces a use-case review or legal advice.
Keep the risk record with the system inventory. A workflow’s rating can change when it gains a new data source or moves from drafting to taking action. The AI automation compliance checklist can help your team connect risk classification with privacy, control records, and review duties.
Milestone: Every workflow has a risk category, a reason for that category, and a clear approval rule tied to its actions.
| Workflow profile | Example | Minimum approval rule |
|---|---|---|
| Lower impact | Drafting an internal knowledge article | Named owner tests it; a person checks content before publication. |
| Moderate impact | Sorting customer requests for staff review | Business and technical owners approve the test plan and escalation path. |
| Higher impact | Changing access to a sensitive system | System owner and security or compliance reviewer approve before release; a person handles exceptions. |
| Material impact on a person | Supporting a decision that may affect an individual | Require documented human review, a clear reason trail, and a defined route to challenge or correct an outcome. |
Step 3: Assign decision rights, owners, and human oversight
Give every workflow a business owner who is accountable for its purpose and impact. Name a technical owner who maintains the system. Then assign a risk or compliance reviewer who can challenge the design and ask for more evidence. One person may hold more than one role in a small team, but the duties still need clear names.
Write down who can approve a workflow at each point: intake, risk classification, release, and major change. Also name the person who can pause it. A committee can set shared policy, but it shouldn’t blur who makes the call for a specific system.
Governance bodies can create, implement, and enforce specific guidelines for AI development and usage. Put those duties into a short charter. Set the meeting cadence, what decisions require a vote, and how unresolved concerns reach an executive sponsor.
Human oversight needs a defined job. Don’t ask a reviewer to “keep an eye on the AI.” Tell them what to check, what counts as an exception, and how to record a decision. In a customer support workflow, for instance, a person might review replies involving refunds or safety concerns while routine drafts follow a lighter check.
Make the handoff visible in the workflow itself. When the system reaches a blocked action, it should stop, show the reviewer the relevant context, and wait for approval. The reviewer should be able to reject the action or correct its inputs. If the workflow cannot explain why it routed a case, add that evidence before launch.
For agents that use tools or move across systems, define what they may access for each task. A broad service account can make an agent’s actions hard to contain. The AI agent governance best practices explain how identity, task-level permissions, human review, and action logs fit together.
Train people on the actual workflow, not only on general AI principles. A support lead needs to know when to override a draft. An engineer needs to know who approves a new tool connection. Zylo Technologies designs custom AI systems and automation with these decision points in mind, so the team that runs the process can understand its duties.
Milestone: Every workflow has named decision-makers, a person with authority to stop it, and a human review path for consequential cases.
Step 4: Put controls into the build, test, and release process
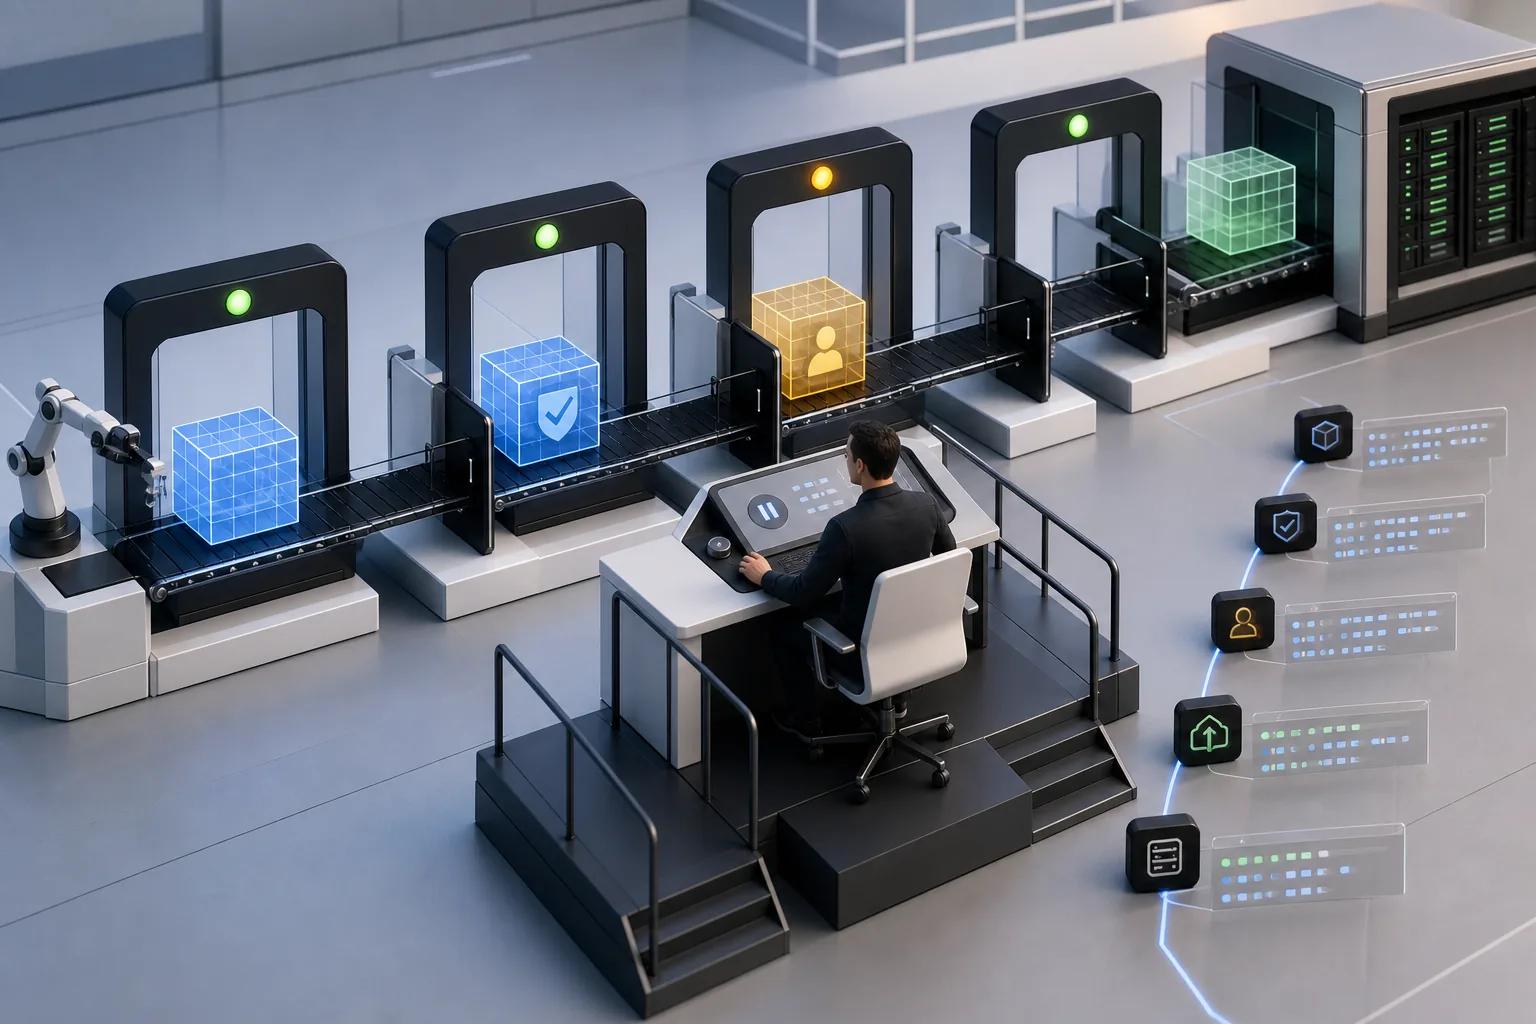
Build governance gates into delivery so a team can’t ship a workflow before it meets its assigned controls. Start at intake: confirm the use case, owner, data sources, risk rating, and approval needs before development begins.
During design, limit access to the data and systems the workflow needs. Use role-based access, which means permissions depend on a person’s or system’s job. Keep test data separate from live records where possible. Track data lineage, the path data takes into and through the system, so a reviewer can see where an input came from.
Before release, test the workflow against expected cases and likely failure cases. Check whether it follows its access rules. Test how it handles missing or conflicting input. For systems that affect people, examine results across relevant groups and decide what evidence would trigger a pause or redesign.
Use a release checklist with a clear stop rule. The checklist might require a risk review, test evidence, approval records, a rollback plan, and a named on-call owner. A prompt edit may need a small test; a new data source or permission may need a deeper security review. Set those change levels before the first update arrives.
Keep an evidence record for each version: what changed, who approved it, which tests ran, and when it went live. This makes it easier to investigate a later error without guessing which version produced the result. It also helps teams compare behavior before and after a change.
Automation can enforce parts of this process. A release pipeline can block deployment if a required review is missing. A registry can prompt owners to renew approvals when a model or connected system changes. Automated checks don’t replace human judgment, but they can catch missing steps before production.
The AI automation deployment checklist offers a way to connect release approvals with testing, security, ownership, and post-launch monitoring. Keep the controls close to the code and workflow, rather than relying on a policy page no one checks during a release.
Milestone: A release cannot pass its required checks without evidence, approval, and a working rollback path.
Step 5: Monitor production, handle incidents, and review the framework
Production governance means checking whether the workflow still behaves as approved. Track operational signals such as completion rate, error rate, exceptions, and human overrides. For AI outputs, also track quality against a set of reviewed examples or task-specific checks.
Log enough detail to reconstruct a consequential action. At a minimum, preserve the input or a safe reference to it, the model or service version, the output, the time, and whether a person changed or approved the result. Protect logs according to your data rules. A record that exposes sensitive information can create a new risk.
Set alerts that lead to a response. A rise in failed runs may point to a broken integration. More overrides may mean the output no longer fits the work. A new access pattern may signal a permission issue. For each alert, define who receives it and what they should do first.
Write an incident plan before the first issue. Name who can pause the workflow, who investigates, and who tells affected teams what happened. Keep a fallback process ready, such as routing requests to a person or returning to a manual queue. After the incident, record the cause, the fix, and what evidence supports restart.
Review the framework on a set schedule and after meaningful changes. Revisit owners, permissions, risk ratings, data sources, and unresolved incidents. A new model version, a new tool call, or a shift from internal use to customer-facing use should trigger a review before the change becomes routine.
Measure whether governance works with indicators tied to action: how many systems have current owners, how many high-impact workflows have approved review paths, how quickly teams resolve incidents, and how often exceptions recur. These measures don’t prove a system is fair or safe by themselves. They show where owners need to investigate.
AI agents may make several calls before completing one request, so monitoring must record the steps that led to the final action. Zylo Technologies has shipped more than 140 systems, and our view is that durable governance depends on those records and clear operating ownership. For ongoing system reviews, use the AI agent lifecycle management guide to connect launch duties with monitoring and change review.
Milestone: Your team can spot a meaningful change, pause the workflow, investigate its record, and approve a safe restart.
AI Automation Governance Framework FAQ
What is an AI automation governance framework?
An AI automation governance framework is a set of rules, roles, and technical controls for how AI workflows are approved and run. It covers the system’s purpose, data access, risk, human review, and production monitoring. The goal is to make responsibility clear and give teams a way to stop or correct unsafe behavior.
What should an AI governance framework include?
It should include a system inventory, risk review, named owners, access rules, human oversight, testing, audit records, and incident steps. Add privacy and bias checks that fit the use case. Then set a review trigger for changes to the model, data, permissions, or workflow purpose.
How do you classify AI automation risk?
Classify risk by the likely impact of a wrong output or action. Consider who could be affected, what data the system uses, whether it acts without review, and whether an error can be reversed. Record the reason for each rating, then tie stronger risks to stricter testing and approval.
Who should own AI automation governance?
Each workflow needs a business owner, a technical owner, and a reviewer with risk or compliance duties. Senior leaders set policy and resolve escalated concerns. A named person should also have authority to pause production use. Small teams can combine roles, but they should document each duty and decision right.
How often should an AI governance framework be reviewed?
Set a regular review schedule based on the workflow’s impact, then review sooner after a meaningful change or incident. A new data source, a change in permissions, or a shift in how people use the system can alter its risk. The owner should record the review and any actions taken.
Conclusion
Build governance into the workflow, not around it. Start by inventorying the systems you already use, then assign an owner and approval rule to each one. If your team needs help turning those rules into production controls, Zylo Technologies can help scope the work; tell us what you’re trying to make possible, and we respond within 48 hours.
Share this article
Author information coming soon.